Cert-In Alerts Banks and Fintechs on AI-Powered Fund Transfer Frauds
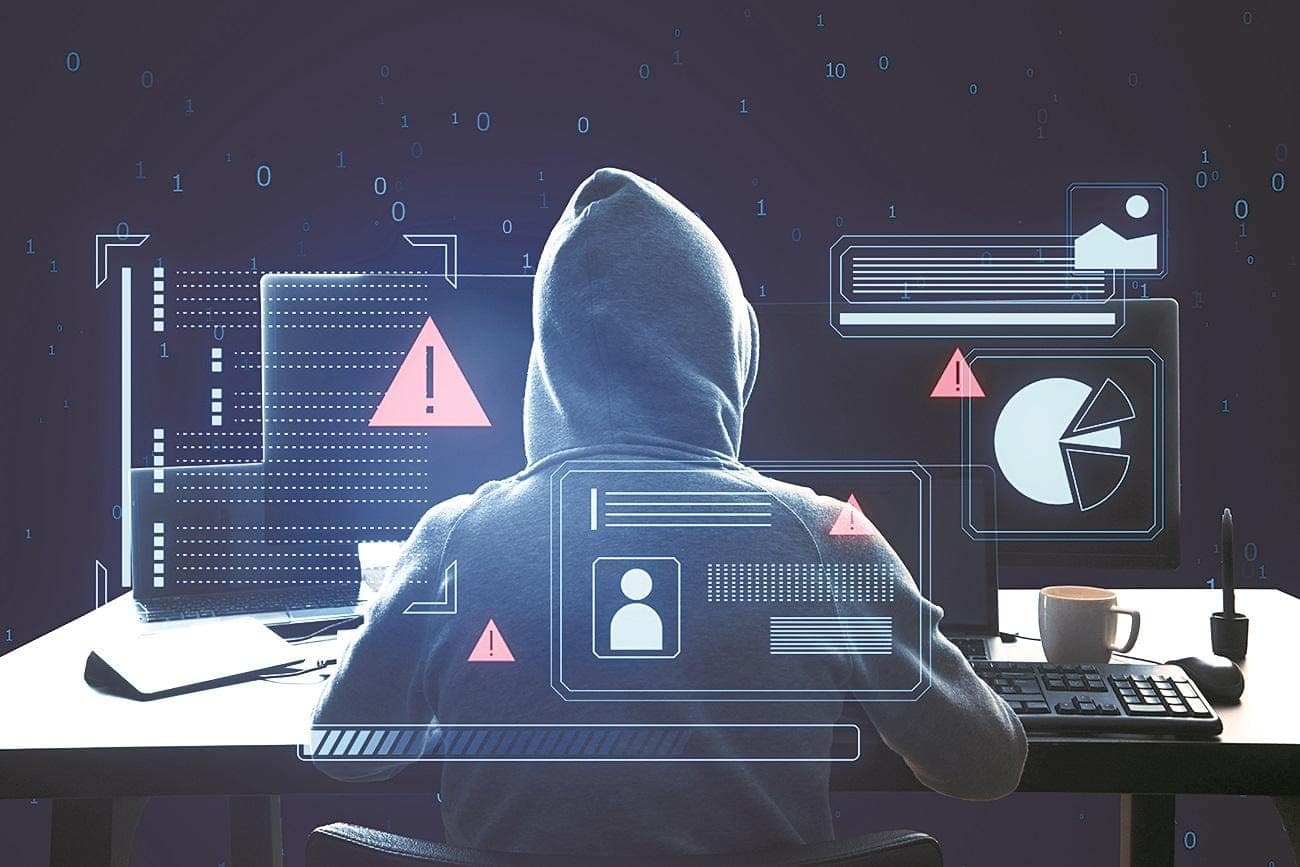
India's cybersecurity authority, the Indian Computer Emergency Response Team (Cert-In), has raised a fresh alarm concerning a surge in unauthorized fund transfers affecting banking and financial services institutions (BFSI). The agency issued a detailed advisory on Wednesday highlighting a sophisticated AI-assisted cyber campaign, dubbed "Crafty Falcon," which leverages publicly accessible AI tools to carry out attacks with high speed and minimal human oversight.
This latest warning updates an earlier alert from October 9, which addressed how threat actors were exploiting payment and disbursement APIs to conduct fraudulent fund transfers within the BFSI sector. Cert-In’s ongoing investigations into reported incidents have revealed an intensification of this cyber threat, affecting not just banks but non-banking financial companies (NBFCs) and fintech startups as well.
According to the advisory, the attacks are persistent and evolving. The Computer Security Incident Response Team-Finance (CSIRT-Fin) continues to receive reports of successful breaches, including from entities previously advised to apply specific remediation measures. Some organizations have been targeted repeatedly, often due to incomplete mitigation of earlier vulnerabilities.
Attackers have strategically timed many of these incursions to coincide with holidays, weekends, and other times when security monitoring tends to be less vigilant. This delay in detection exacerbates the damage and complicates response efforts.
AI Tools Empowering Cybercriminals
Cert-In’s analysis identified multiple AI-driven offensive security tools facilitating these attacks. Notable among them are the ARTEX suite of large language model (LLM)-based utilities, the PentAGI autonomous multi-agent penetration testing framework, the Cairn attack search engine, and the CyberStrikeAI platform. These sophisticated tools can autonomously execute full attack chains, rapidly generate and refine numerous customized attack scripts, and adapt their payloads dynamically based on system responses.
Methods Used to Breach Financial Systems
The advisory details several tactics employed by attackers to compromise financial institutions. One common method involves exploiting internet-facing testing and staging environments, which often share credentials, tokens, or network connections with live production systems. By leveraging these weaknesses, attackers gain unauthorized access to critical infrastructure.
Cloud environments have also been targeted extensively. Threat actors abuse cloud management services such as Amazon Web Services (AWS) Systems Manager and Lambda functions to execute commands and deploy malicious payloads while camouflaging their activities within legitimate operations. In some cases, attackers reverse-engineer application code to create modified packages that initiate unauthorized API calls.
Attempts to bypass IP-based security controls have been observed, with attackers routing requests through trusted third-party services. Fraudulent fund transfers are sometimes tested with micro-value transactions as low as ₹1 before larger sums are moved. Payment aggregator merchant settlement APIs have also been exploited for this purpose.
The advisory also highlights the exploitation of recently disclosed vulnerabilities, including file upload flaws and deserialization issues affecting PHP and Node.js applications. Cryptocurrency exchanges and virtual digital asset service providers have not been spared, with attackers stealing wallet keys and siphoning off digital assets.
Recommended Security Measures for BFSI Entities
Cert-In strongly urges banks, fintech companies, and other BFSI institutions to enhance continuous security monitoring. Organizations should increase staffing and lower alert thresholds during weekends and holidays to promptly detect suspicious activity. Real-time oversight of cloud audit logs and tighter restrictions on cloud management services, including disabling internet access for serverless functions by default, are critical.
Isolating testing and staging environments from production systems is essential, as is avoiding credential and API key sharing. Internet-facing applications require strengthened security controls, including server-side validation for transactions, API request signing with nonces and timestamps, and app attestation to identify tampered or repackaged applications.
Faster patching cycles are necessary, especially for vulnerabilities related to file uploads and deserialization. Institutions should replace IP-based access controls with identity-based safeguards for shared third-party services.
Transaction monitoring should flag patterns such as small-value transfers to new beneficiaries followed by large transactions, which may indicate fraudulent behavior. Cryptocurrency platforms are advised to secure wallet keys using hardware security modules or cold wallets, enforce multi-signature withdrawal approvals, and monitor unusual withdrawal patterns.
Additionally, restricting unauthorized AI-driven security and attack tools on corporate systems and monitoring the use of LLM APIs can help mitigate risks. Adopting zero-trust security models, micro-segmentation, and identity-based access controls further strengthens defenses.
In case of suspected breaches, affected organizations should isolate compromised systems, preserve forensic evidence and logs, rotate credentials, and report incidents promptly to Cert-In or CSIRT-Fin.
This advisory from Cert-In underscores the growing challenges posed by advanced AI-powered cyber threats targeting the BFSI sector. With financial institutions increasingly reliant on cloud infrastructure and digital payment systems, maintaining rigorous security protocols has become vital to safeguard customer assets and data integrity. The evolving threat landscape demands vigilance, rapid response, and continuous improvement of cybersecurity measures across the financial ecosystem.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0






Comments (0)